
Lexi runs in a secure, isolated AWS environment. Every action is permissioned, approved and logged, and your customer data never leaves the platform.
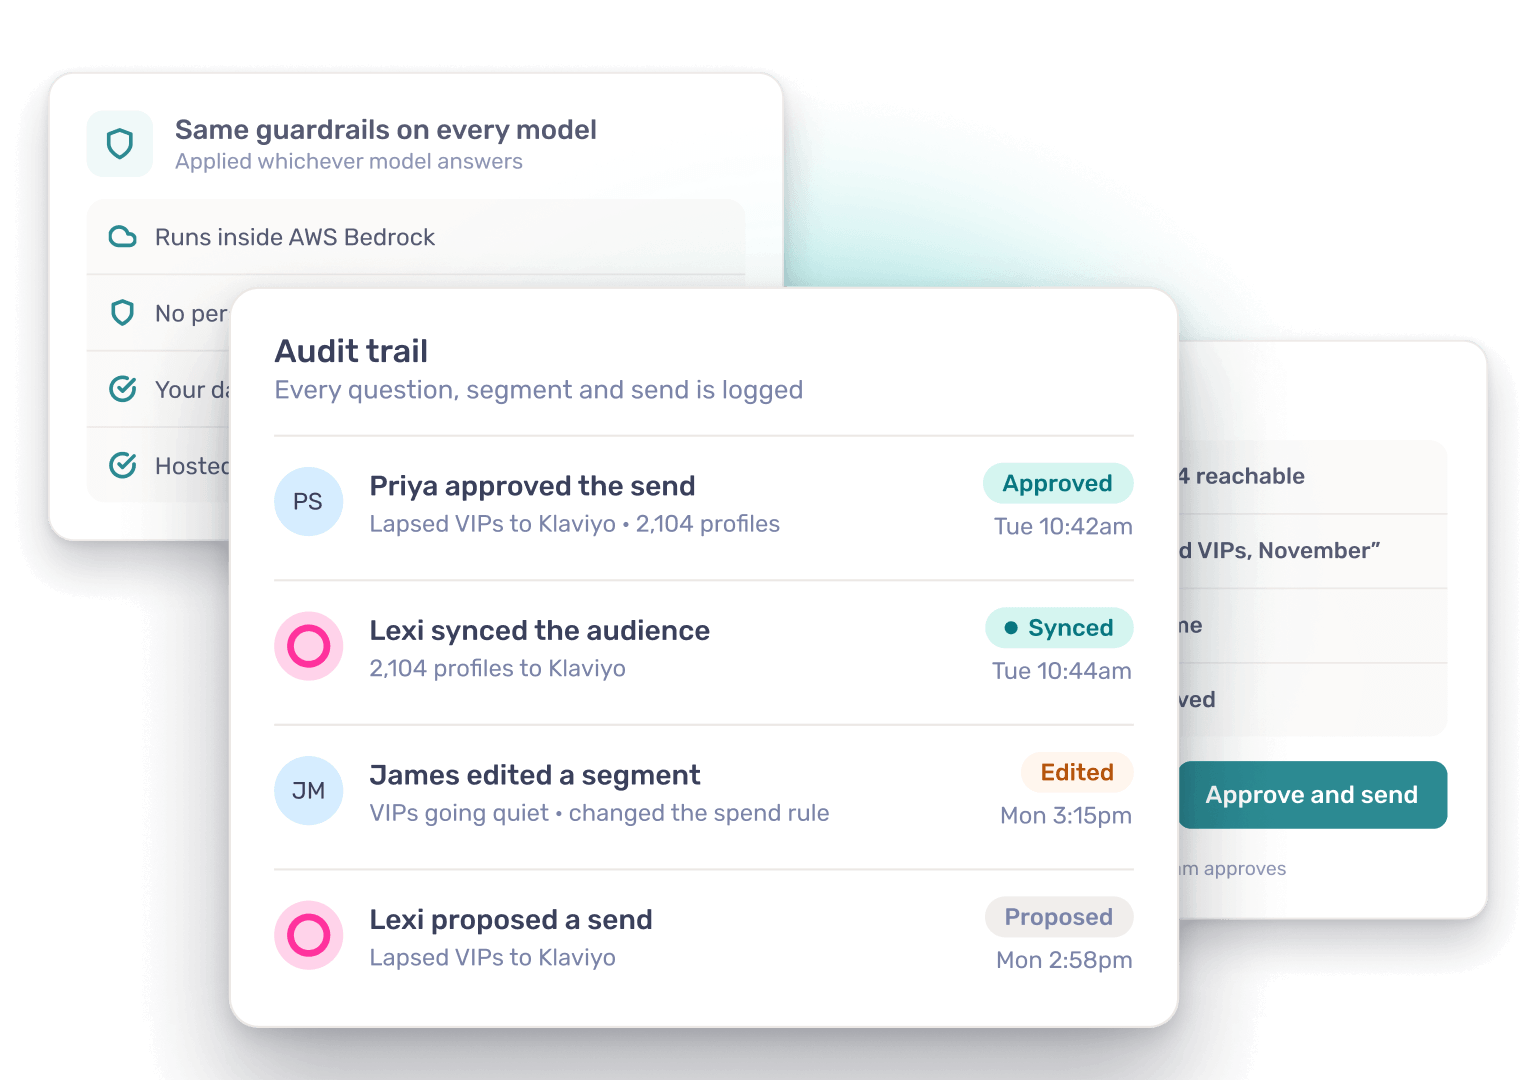
Each client's data sits in its own isolated environment, in AU or US regions. Nothing is sent to an external model, and no personal information is used in AI processing.
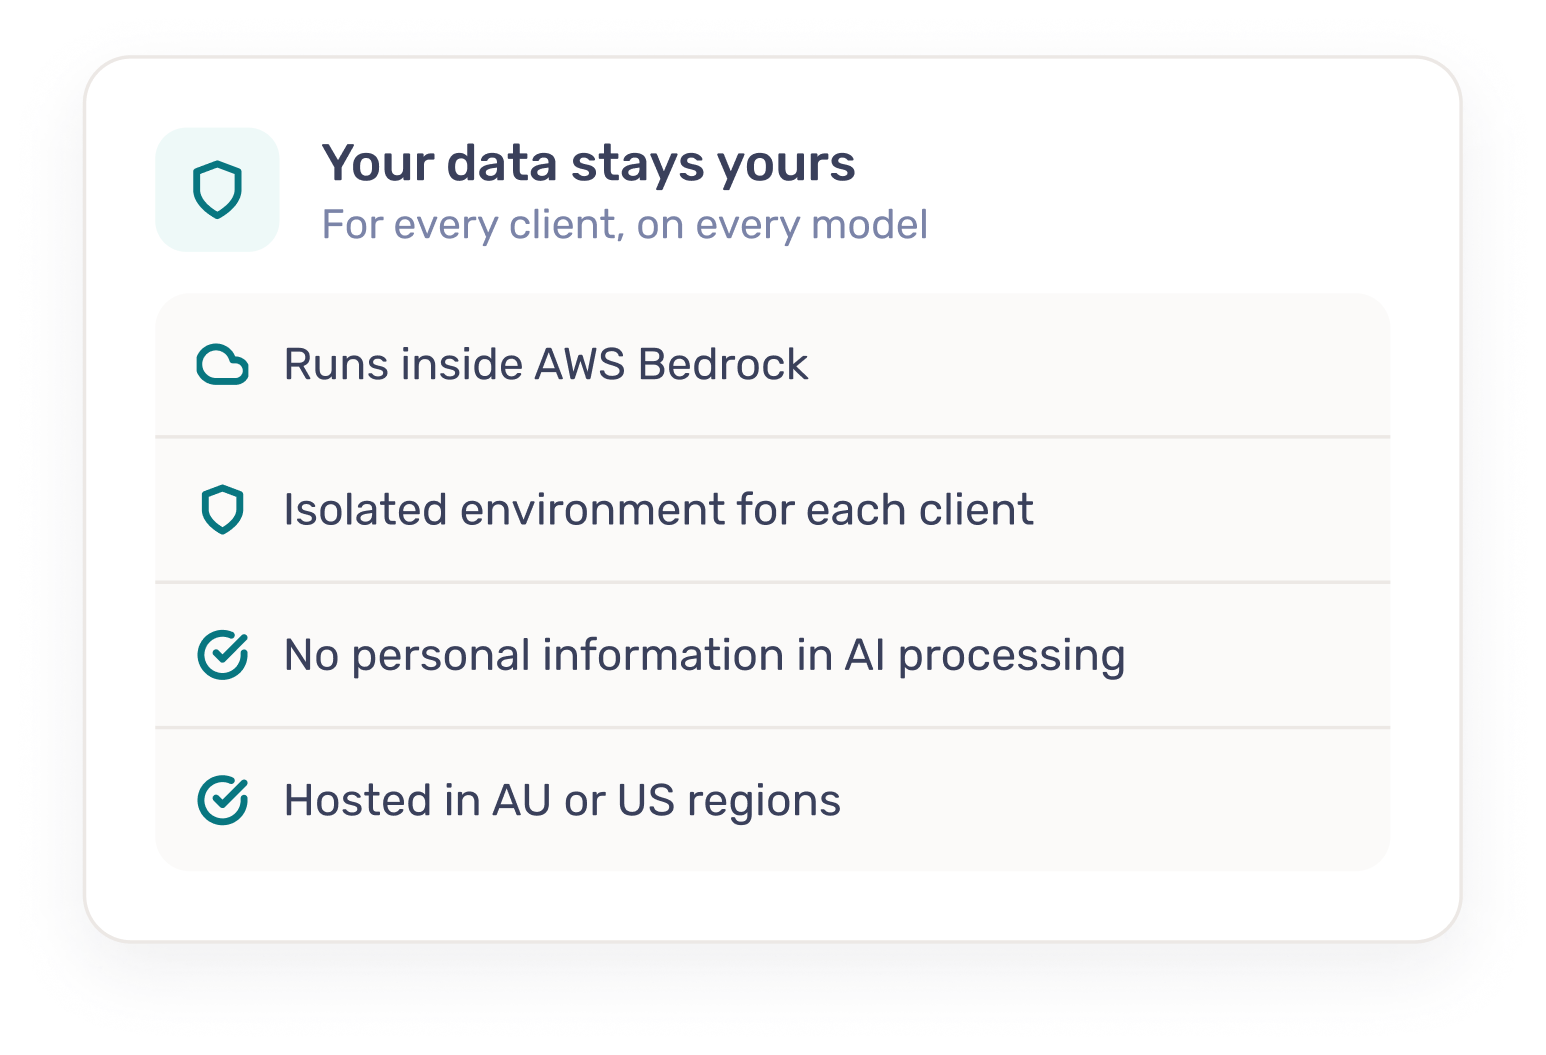
Lexi proposes and your team decides. Low-risk actions go ahead, and anything that reaches customers waits for sign-off.
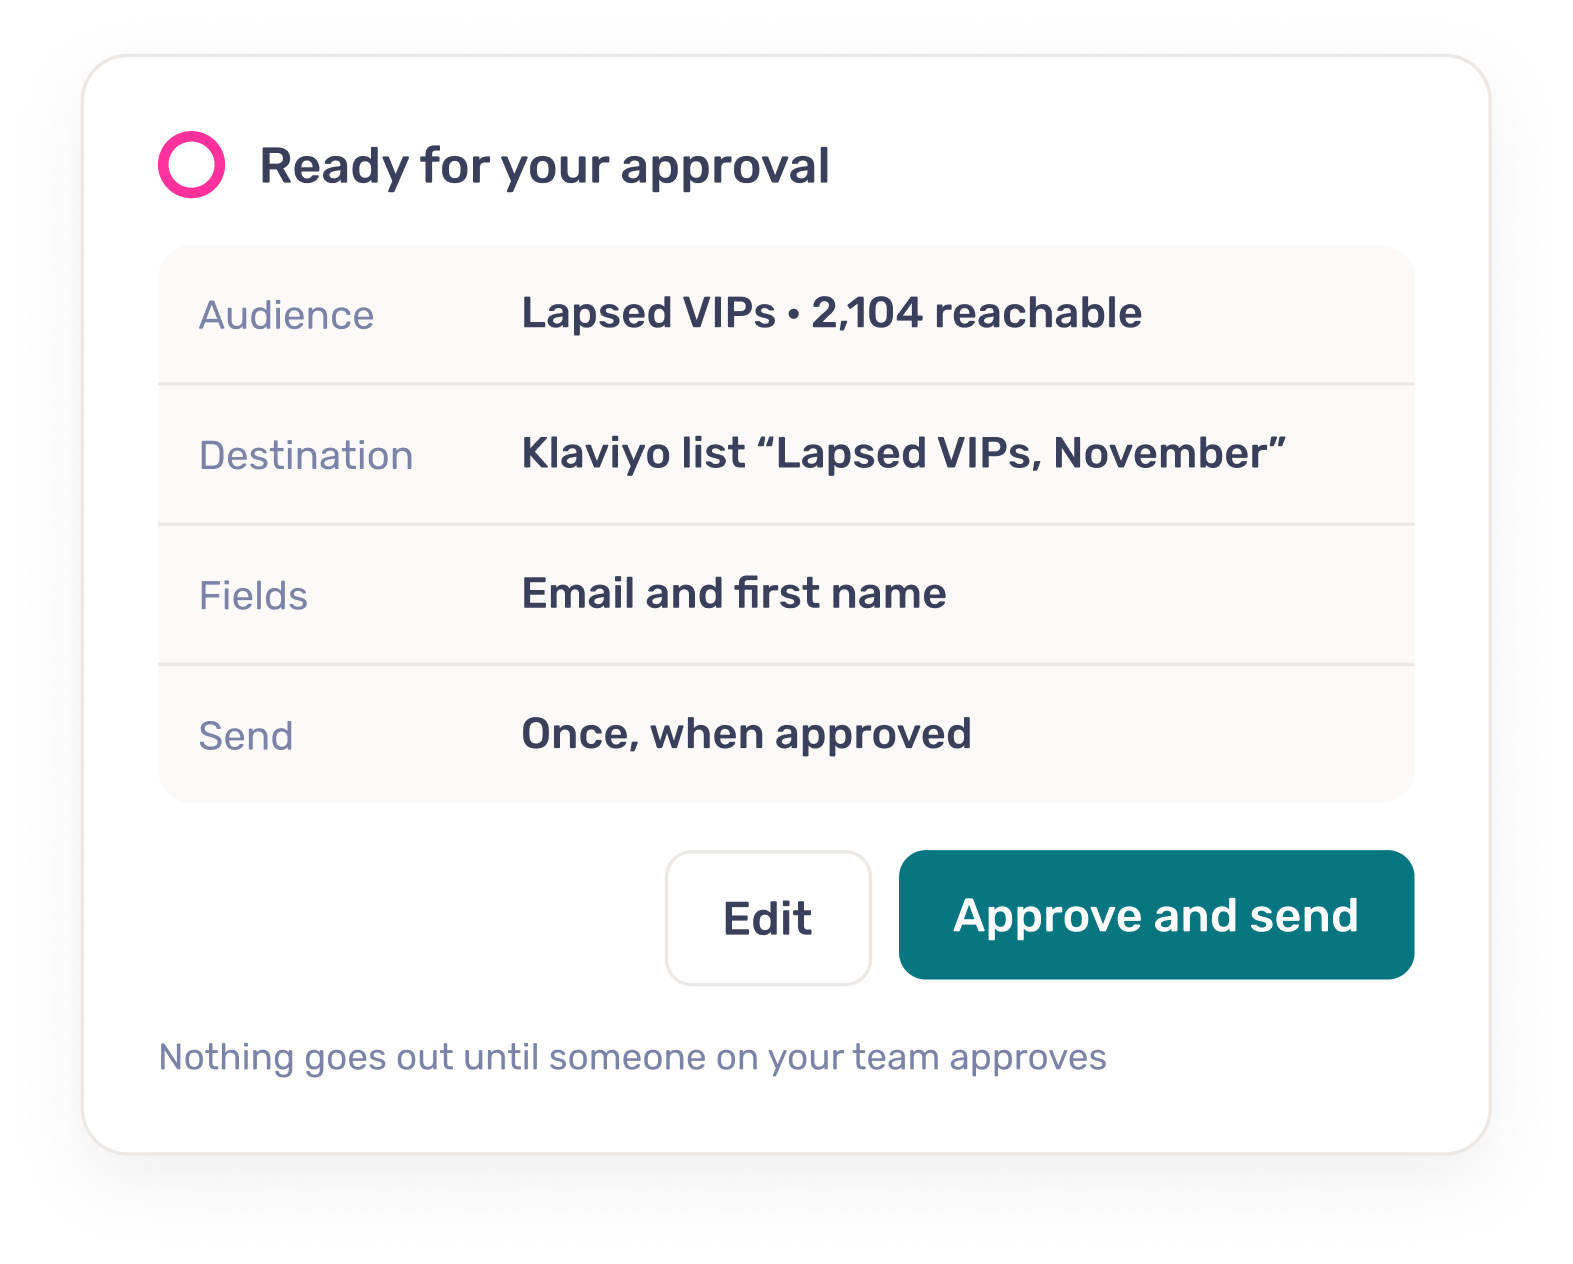
Permissions control who can see and do what. Every question, segment and send is logged, so you always know who did what and when.
Lexi runs in dedicated AWS accounts, separate from other systems, with separate storage and access policies for each client. Every code change passes automated security checks and a human review before it reaches production.
Certification SOC 2, with GDPR and CCPA compliance
AI runtime AWS Bedrock, with no data sent to external model providers
Privacy No PII used in AI processing
Isolation A dedicated environment and access policy per client
Control Role-based permissions and approval on every activation
Audit Every action logged and reviewable
Yes. Lexi runs inside a secure AWS Bedrock environment, your data never leaves the platform and nothing is shared with external models. Lexer is SOC 2 certified.
No. Your data is never sent to an external model provider, so it can't be used to train their models.
Anything that reaches customers, such as a send to Klaviyo, needs approval from someone on your team first.
Visit the Lexer Security Centre for certifications, policies and how to request documentation.

Book a demo with Lexer
30 min • Video call • No commitment required
Loading available times…